 01 / 04
Firewall rules
What we deliverLayer 3 and Layer 7 rules by address, port and application.
Why it matters
Only the traffic each system needs gets through, and every rule change is logged and backed up.
Security for your business network and every camera, reader and intercom on it.
installations over 10+ years
support for managed-service clients
Rated 4.9/5 by 110+ NYC corporations
Operating throughout New York
Our cybersecurity services in NYC start with cameras, readers and intercoms: computers nobody treats as computers.
On a flat network, one weak device reaches everything. After segmentation, a compromised camera reaches only its recorder, which helps stop a breach spreading. Staff, guest, video, access control, intercom and management traffic each get their own network.
Remote viewing keeps working without exposing the recorder. Each user reaches only the system they need: a facility manager reaches the video platform and nothing else. Outside vendors get named, time-limited accounts, so no shared logins are left behind.
Usually IT and the security vendor each assume the other owns the cameras' firmware and passwords. We own both the device and the firewall, so the gap has an owner. We build to your policies, record every change and hand over full documentation.
For cybersecurity in New York under NYDFS Part 500 or the NY SHIELD Act, our network security services support your program. Your compliance team owns it, and we do not certify compliance.
Managed firewall services keep edge policy correct over time, on next-generation firewalls such as the Cisco Meraki MX.
01 / 04Layer 3 and Layer 7 rules by address, port and application.
Only the traffic each system needs gets through, and every rule change is logged and backed up.
02 / 04Content filtering, intrusion prevention and Advanced Malware Protection.
These run on the Meraki MX with Advanced Security licensing, and Meraki Auto VPN links your locations site to site.
 03 / 04
Cisco Secure Client (formerly AnyConnect) on the MX, authenticated against your directory.
Multi-factor authentication runs through your identity provider, following zero-trust principles: every user is verified before they reach anything.
 04 / 04
Offline devices and configuration changes flagged from the cloud dashboard.
Your team sees problems as they happen. Existing managed-service clients also get 24/7 support, with a 4-hour response on critical failures.
Pacha NYC shows the network and security delivered together; Lexington School shows NDAA-compliant access control.
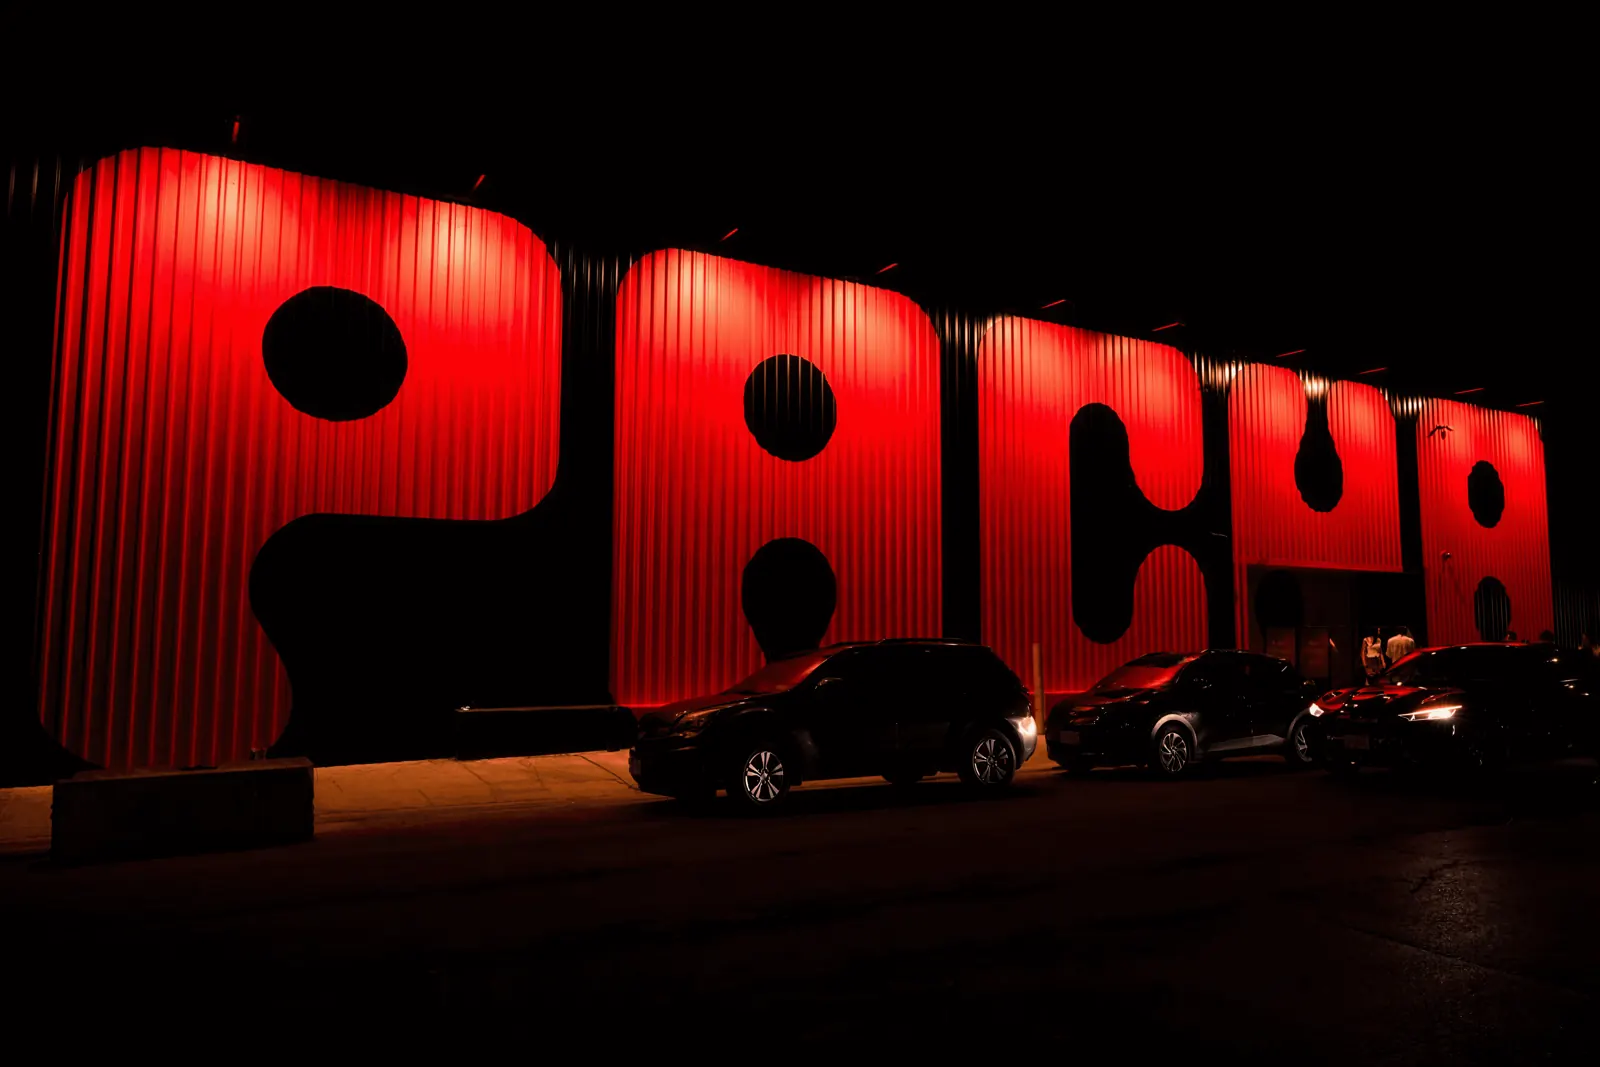
Two venues' network and security systems delivered by one team.
IT infrastructure programming, structured cabling and fiber, integrated access control and over 200 AI-powered cameras across Brooklyn Hall and Pacha, with 25+ technicians working simultaneously and ongoing support.
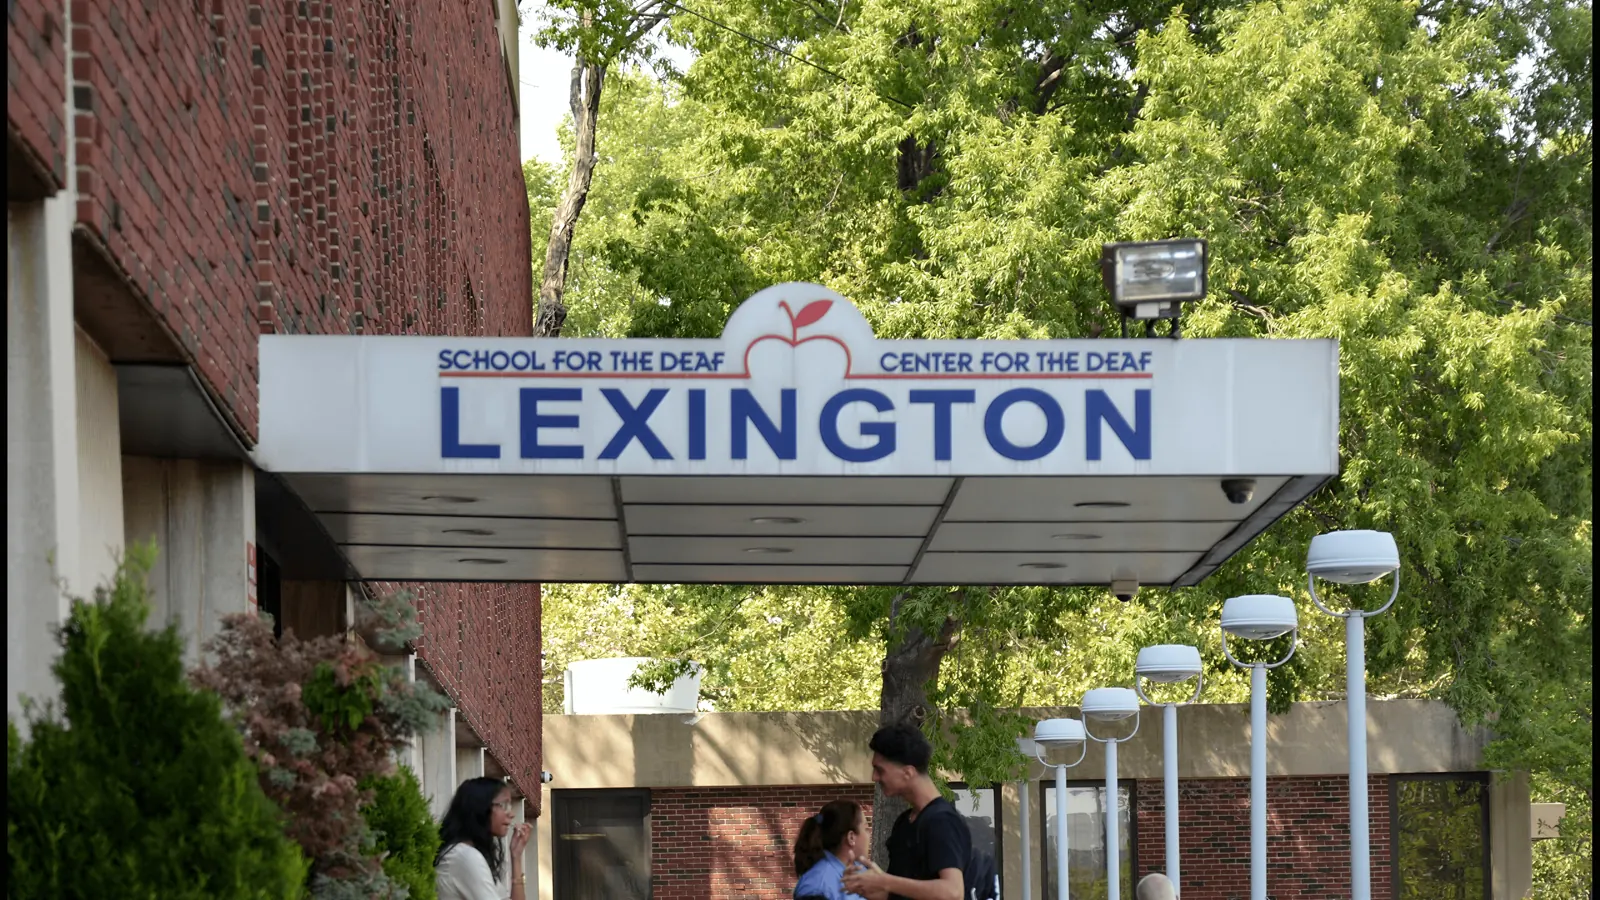
Compliant, on-premises access control with accessible entry.
Electrified retrofit hardware, NDAA-compliant on-premises access control and two ADA-compliant swinging doors.
What do your security systems expose?
We will review what runs on your network and show you the gaps.
Hardening closes the gaps firewalls cannot see, with one baseline on every device we install or take over.
 01 / 04
Its own administrator password on every device, with UPnP, Telnet and FTP turned off.
A leaked password exposes one device, not every camera, and fewer running services means fewer ways in.
 02 / 04
Updates on a schedule, tested on one unit before the rest.
Known flaws are closed without breaking the systems that depend on the device.
 03 / 04
HTTPS for management, and OSDP Secure Channel instead of Wiegand.
Traffic between readers and controllers, and to management screens, is encrypted in transit.
04 / 04NDAA-compliant cameras only, from Axis and Genetec.
Section 889 of the 2019 NDAA bars federal agencies and grant recipients from buying covered equipment, including Hikvision, Dahua and Hytera video surveillance and Huawei and ZTE telecom equipment.
Each class of device gets its own network, and this is what each one may reach.
| Network | What is on it | What it may talk to |
|---|---|---|
| Staff | Laptops, phones, printers | Business systems and filtered internet |
| Video | Cameras and recorders | The recorder only |
| Access control | Door controllers, readers | Its server or cloud service only |
| Intercom and IoT | Intercoms, sensors, AV | Their own platform and named integrations |
| Guest | Visitor devices | Internet only, clients isolated |
| Management | Switch and firewall management | Authorized administrators only |
Staff wireless uses WPA3 and 802.1X, so network access ends the day someone leaves.
Four steps, from what is on your network today to records your team keeps.
Every device on the network listed, with its credentials, firmware and exposure.
Each class of device moved to its own network, denied by default.
Unique credentials, tested firmware, encrypted connections and unused services off.
Segmentation diagrams, rule descriptions and change logs handed to your team.
FAQs
The cybersecurity services we provide in NYC cover the network and the security systems on it. That means managed firewalls, segmentation, secure remote access, device hardening and monitoring.
We are a security integrator that secures the networks we build. We also install the cameras and access control on them.
Yes, we offer managed firewall services on next-generation firewalls such as the Cisco Meraki MX. That covers rules, content filtering, intrusion prevention, VPN and change control.
Physical security cybersecurity matters because cameras, door controllers and intercoms are network devices with credentials and firmware. Each one stays on the network for years.
We can help with the network and security-system controls behind NYDFS Part 500 or other New York requirements. Our documentation supports your program; your compliance team owns it.
No, we do not replace your IT team or provider. We secure the network infrastructure and security systems, and hand over full as-built documentation.
Tell us which systems you run. We'll give you a prioritized list of fixes.